On-Demand Webinar
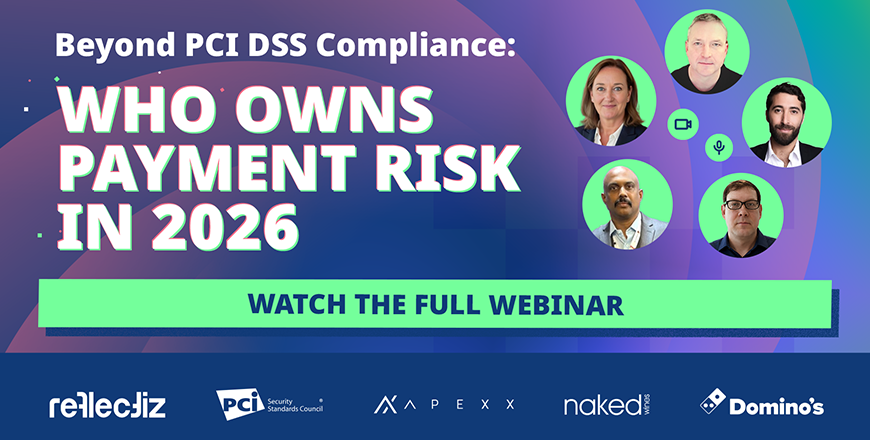
Beyond PCI DSS Compliance: Who Owns Payment Risk in 2026
Watch Now
Watch this executive panel discussion uniting the standards body, the payments industry, and enterprise security to confront the accountability gap that PCI DSS 4.0.1 compliance alone can’t close.
Panelists
Una Dillon, Regional Director Europe, PCI Security Standards Council
Una brings the standards perspective — what PCI DSS 4.0 requires, where interpretation matters, and what the Council sees as the next frontier for payment security.
Deepak Kumar Ramanujam, Head of Information Security at APEXX Global
Deepak offers a payments industry view — how orchestration layers, acquirers, and PSPs think about risk distribution and where technical accountability sits in modern payment stacks.
Mark Barry, Senior Security Operation Manager at Domino’s Pizza UK & Ireland Ltd
Mark Barry Oversees security at one of the UK’s busiest digital ordering platforms, Mark knows firsthand what payment risk looks like at scale and what it takes to stay ahead of it.
Pete Chenery, Global Head of Cyber Security at Naked Wines
With a career spanning over two decades, Peter’s expertise lies in integrating enterprise security solutions and IT governance frameworks. As a Group Architect at Somewhere Great, he shares insights on aligning business objectives with advanced security measures, guiding organizations to enhance their resilience against modern threats.
Host:
Leor Eliashiv, UK and Ireland Country Manager at Reflectiz
About the executive panel discussion
PCI DSS 4.0.1 introduced requirements designed to close critical security gaps in the payment ecosystem. But certification does not equal protection. Third-party scripts, invisible redirect chains, and real-time data exposure on checkout pages continue to put cardholder data at risk, often outside the boundaries of what any single team owns or monitors.
This panel brought together four senior voices. From standards, payments, and enterprise security, to examine where formal compliance ends and genuine accountability must begin.
What You’ll Learn
- Where PCI DSS 4.0.1 draws the line and where risk does not follow it
- How third-party scripts and pixel tracking create exposure that compliance tools miss
- Who bears accountability when payment data is compromised through the client side
- What security and compliance leaders should be doing now to close the gap